Strictly necessary cookies keep the site working. Optional analytics cookies load only with your consent. Privacy policy
Built in the UAE for the GCCLive now
The standard for compliance in the Gulf.
Organisations across the GCC trust their most sensitive obligations to spreadsheets. MIZAN COMPLY replaces them with one sovereign platform for every major Gulf framework, from NESA IAS and ADHICS to NCA ECC and SAMA CSF, backed by the security specialists at SIAN Cyber Security.
- 10 frameworks ready
- 655 requirements mapped
- Hosted on UAE soil
- UAE, KSA and international
- Exhibitor, GISEC Global 2026
- Powered by SIAN Cyber Security
- Tailored to your organisation
The stakes
Every auditor asks three questions.
If answering any of them takes more than a minute, your program is exposed. Findings, delayed certifications and lost contracts all start here.
- I“Who owns this control?”
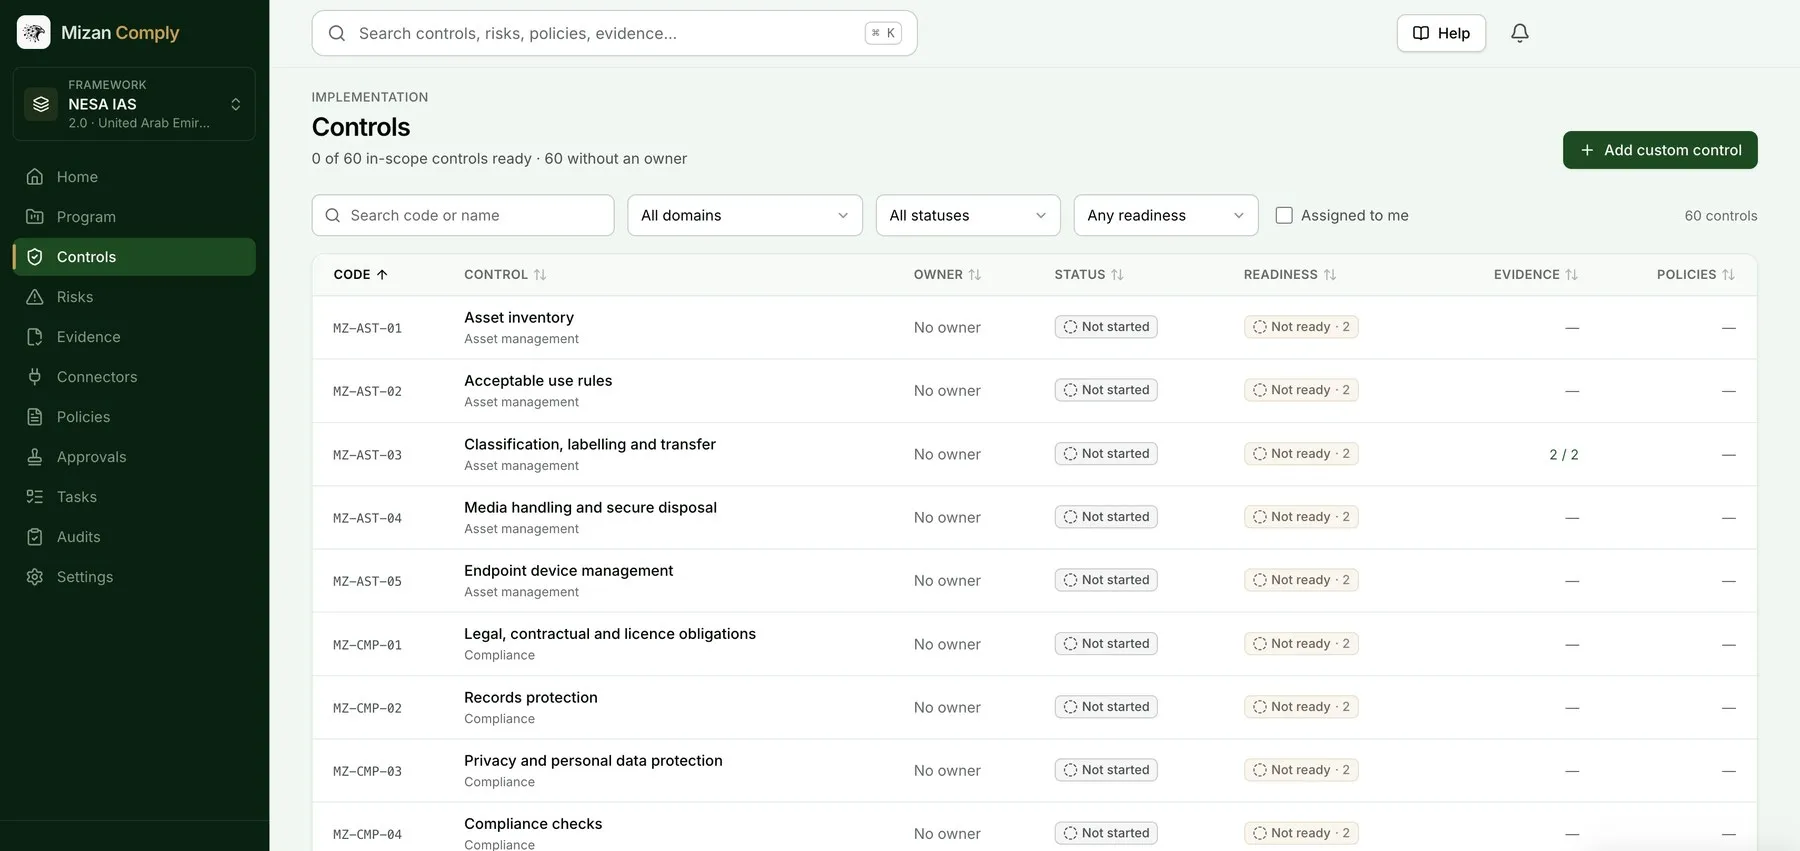
In most teams, nobody knows for sure. In MIZAN COMPLY, every control has a named owner and a live status.
- II“Show me the evidence.”
No more digging through inboxes. Evidence is linked to the controls it proves, with expiry dates tracked for you.
- III“When was this last approved?”
Every policy, risk and decision carries a sign off trail your auditor can follow from start to finish.
One platform that answers before anyone asks.
Frameworks, controls, risks, evidence, AI drafted policies, approvals, audits and purple team findings. Connected in one place, so your readiness is always visible and always defensible.
Risk management
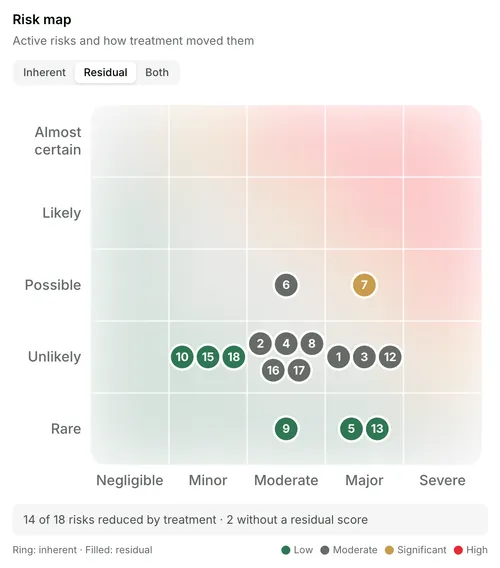
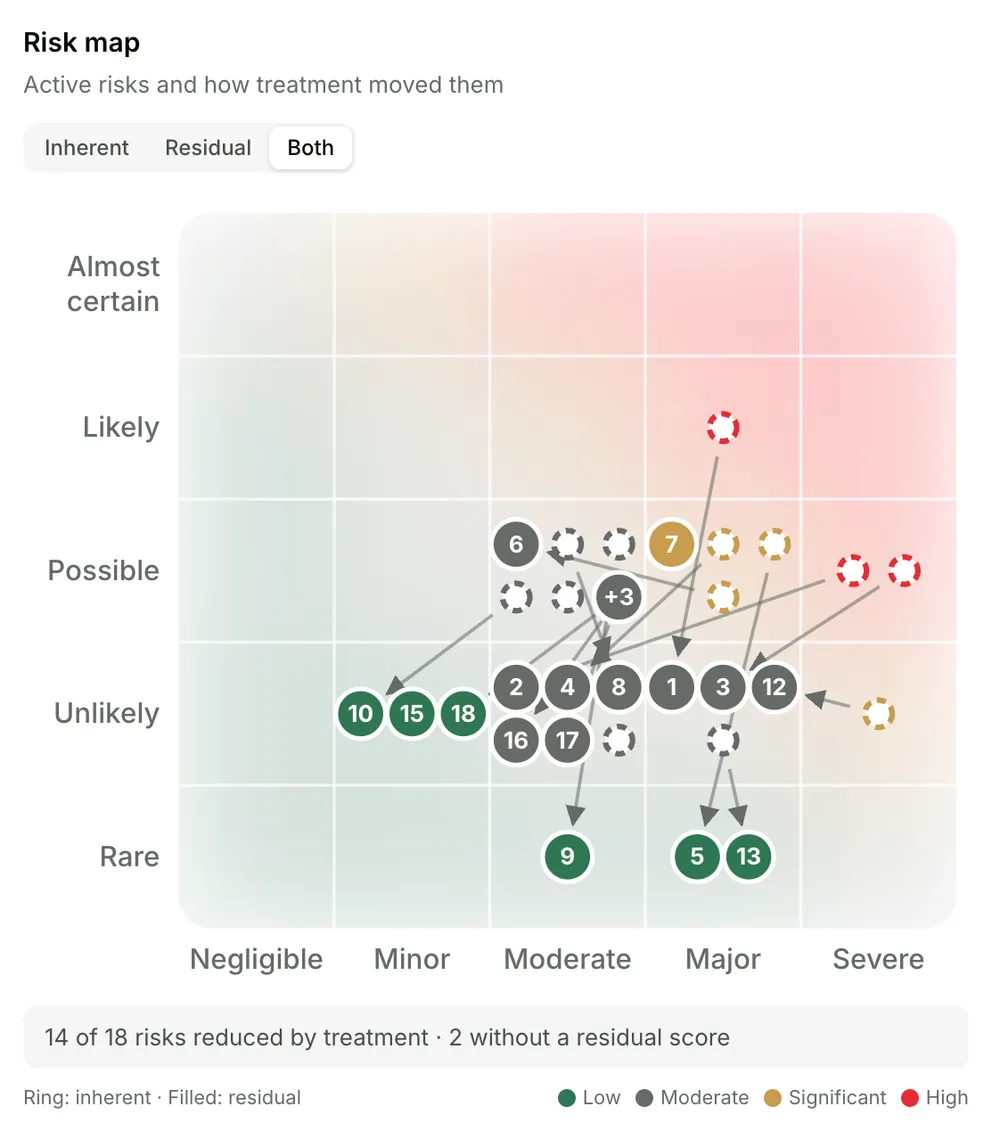
See exactly how treatment moves your risk.
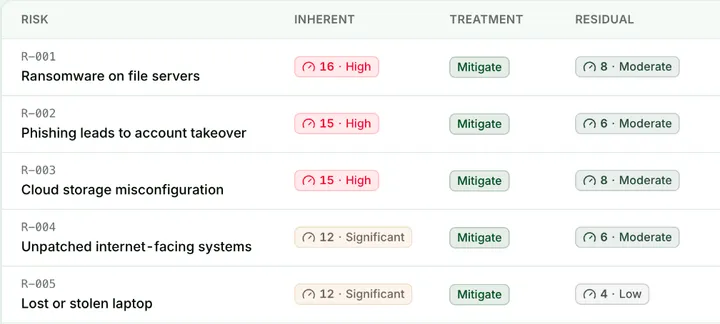
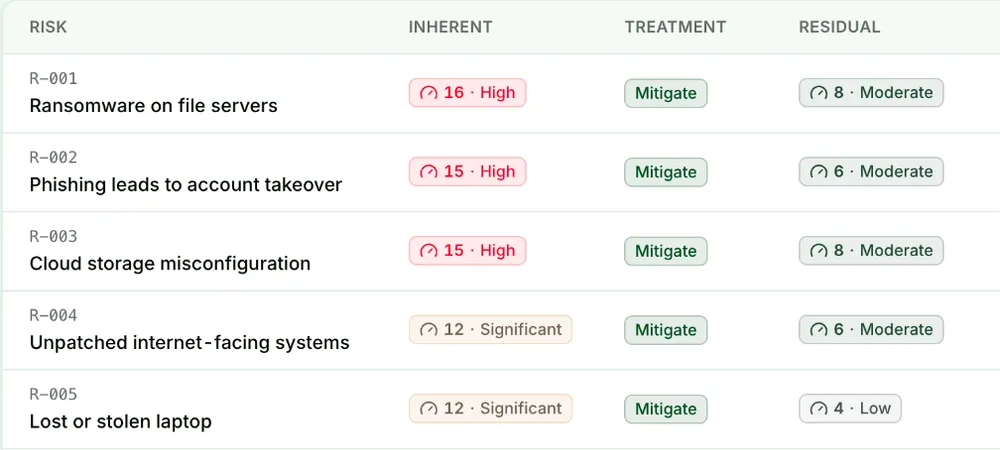
Score every risk by likelihood and impact, plan its treatment, and watch it move from inherent to residual on one live map. Starting from zero? Suggest from library adds the risks that fit your context in a single click.
- Inherent and residual risk on one map
- Suggest risks from a ready made library
- Treatment plans with owner sign off
The platform
Evidence in. Audit readiness out.
Nine capabilities that work as one system of record, so every control, risk, policy and finding stays connected from the day you start to the day you pass.
- 01
GCC framework coverage
Ten Gulf and international frameworks on day one. Every control, domain and mandatory requirement pre loaded, with no manual setup.
- 02
Controls tracking
A real time compliance dashboard. Filter by P1, P2 or P3 priority, status, owner and due date, and update controls in bulk.
- 03
Risk register
Inherent and residual scoring, treatment plans and a library of risks that fit your context.
- 04
Evidence management
Upload documents and screenshots, link them to controls and track expiry dates. Reviewers approve or reject with notes on a full audit trail.
- 05
AI policy generator
Choose a policy type and a framework. Get a complete, editable policy tailored to your industry, company size and GCC requirements.
- 06
Audit ready reports
Export your full compliance posture as a PDF or evidence package, with control level detail and linked evidence. Exactly what auditors need.
- 07
Purple team integration
Map security assessment findings directly to compliance controls. See which controls are at risk from real security gaps, not just missing paperwork.
- 08
Approvals and tasks
Request sign off, assign work and set deadlines, with every decision recorded for your auditor.
- 09
Audits and findings
Plan your audits, track every finding to closure and keep open items visible until they are resolved.
Frameworks
Every Gulf framework. Ready to run.
From the UAE and Saudi Arabia to the international standards your buyers ask for. Need something else? Start a new program from the library, or we’ll build one around your sector.
- frameworks ready to run
- 10
- requirements mapped
- 655
- controls ready to assign
- 522
| Framework | Jurisdiction and authority | Requirements | Controls |
|---|---|---|---|
NESA IAS Version 2.0 | United Arab Emirates UAE Cyber Security Council (formerly NESA) | 122 | 170 |
UAE PDPL 2021 | United Arab Emirates UAE Data Office | 20 | 27 |
ADHICS Version 2 | Abu Dhabi, United Arab Emirates Department of Health, Abu Dhabi | 54 | 45 |
NCA ECC 1.0 (2018) | Saudi Arabia National Cybersecurity Authority (NCA) | 114 | 59 |
Saudi PDPL 2021 | Saudi Arabia Saudi Data and AI Authority (SDAIA) | 37 | 32 |
NCA CCC CCC 2:2024 | Saudi Arabia National Cybersecurity Authority (NCA) | 55 | 63 |
SAMA CSF 1.0 (2017) | Saudi Arabia Saudi Central Bank (SAMA) | 36 | In progress |
ISO/IEC 27001 2022 | International ISO/IEC | 127 | 60 |
ISO/IEC 27090 2026 | International ISO/IEC | 16 | 22 |
ISO/IEC 42001 2023 | International ISO/IEC | 74 | 44 |
Data sovereignty
62%
of MEA cybersecurity spend goes on premises because of data sovereignty laws. The region has spoken. We listened.
Your data never leaves the Emirates.
- Hosted on UAE soil
- Dedicated in country infrastructure
- Single region
- No inter region routing
- Private by design
- No third party data sharing
- Built on UAE law
- Federal Decree Law No. 45
What we stand for
Compliance is not about avoiding penalties. It’s about earning trust.
- 01
Trust above everything
Consistency, transparency and accountability in all we deliver.
- 02
Compliance with purpose
Practical compliance that creates measurable business value.
- 03
Security by design
Protection built into every process, never bolted on.
- 04
Clarity in complexity
Complex regulation made simple enough to act on.
- 05
Long term partnership
We grow with you across your compliance journey.
When the auditor calls, be the one who is ready.
Register now
Our team reviews every registration and sets up your workspace personally.